Whoa!
I remember holding my first Tangem card and thinking it was almost too simple.
It fit in my wallet like a credit card, but it promised something way more valuable than convenience: true cold storage without the fuss.
At first glance it felt like magic—tap your phone, sign a tx, done—though actually the security model is subtle and worth unpacking.
Here’s the thing. the simplicity masks design choices that change how you should think about backups, loss, and long-term custody.
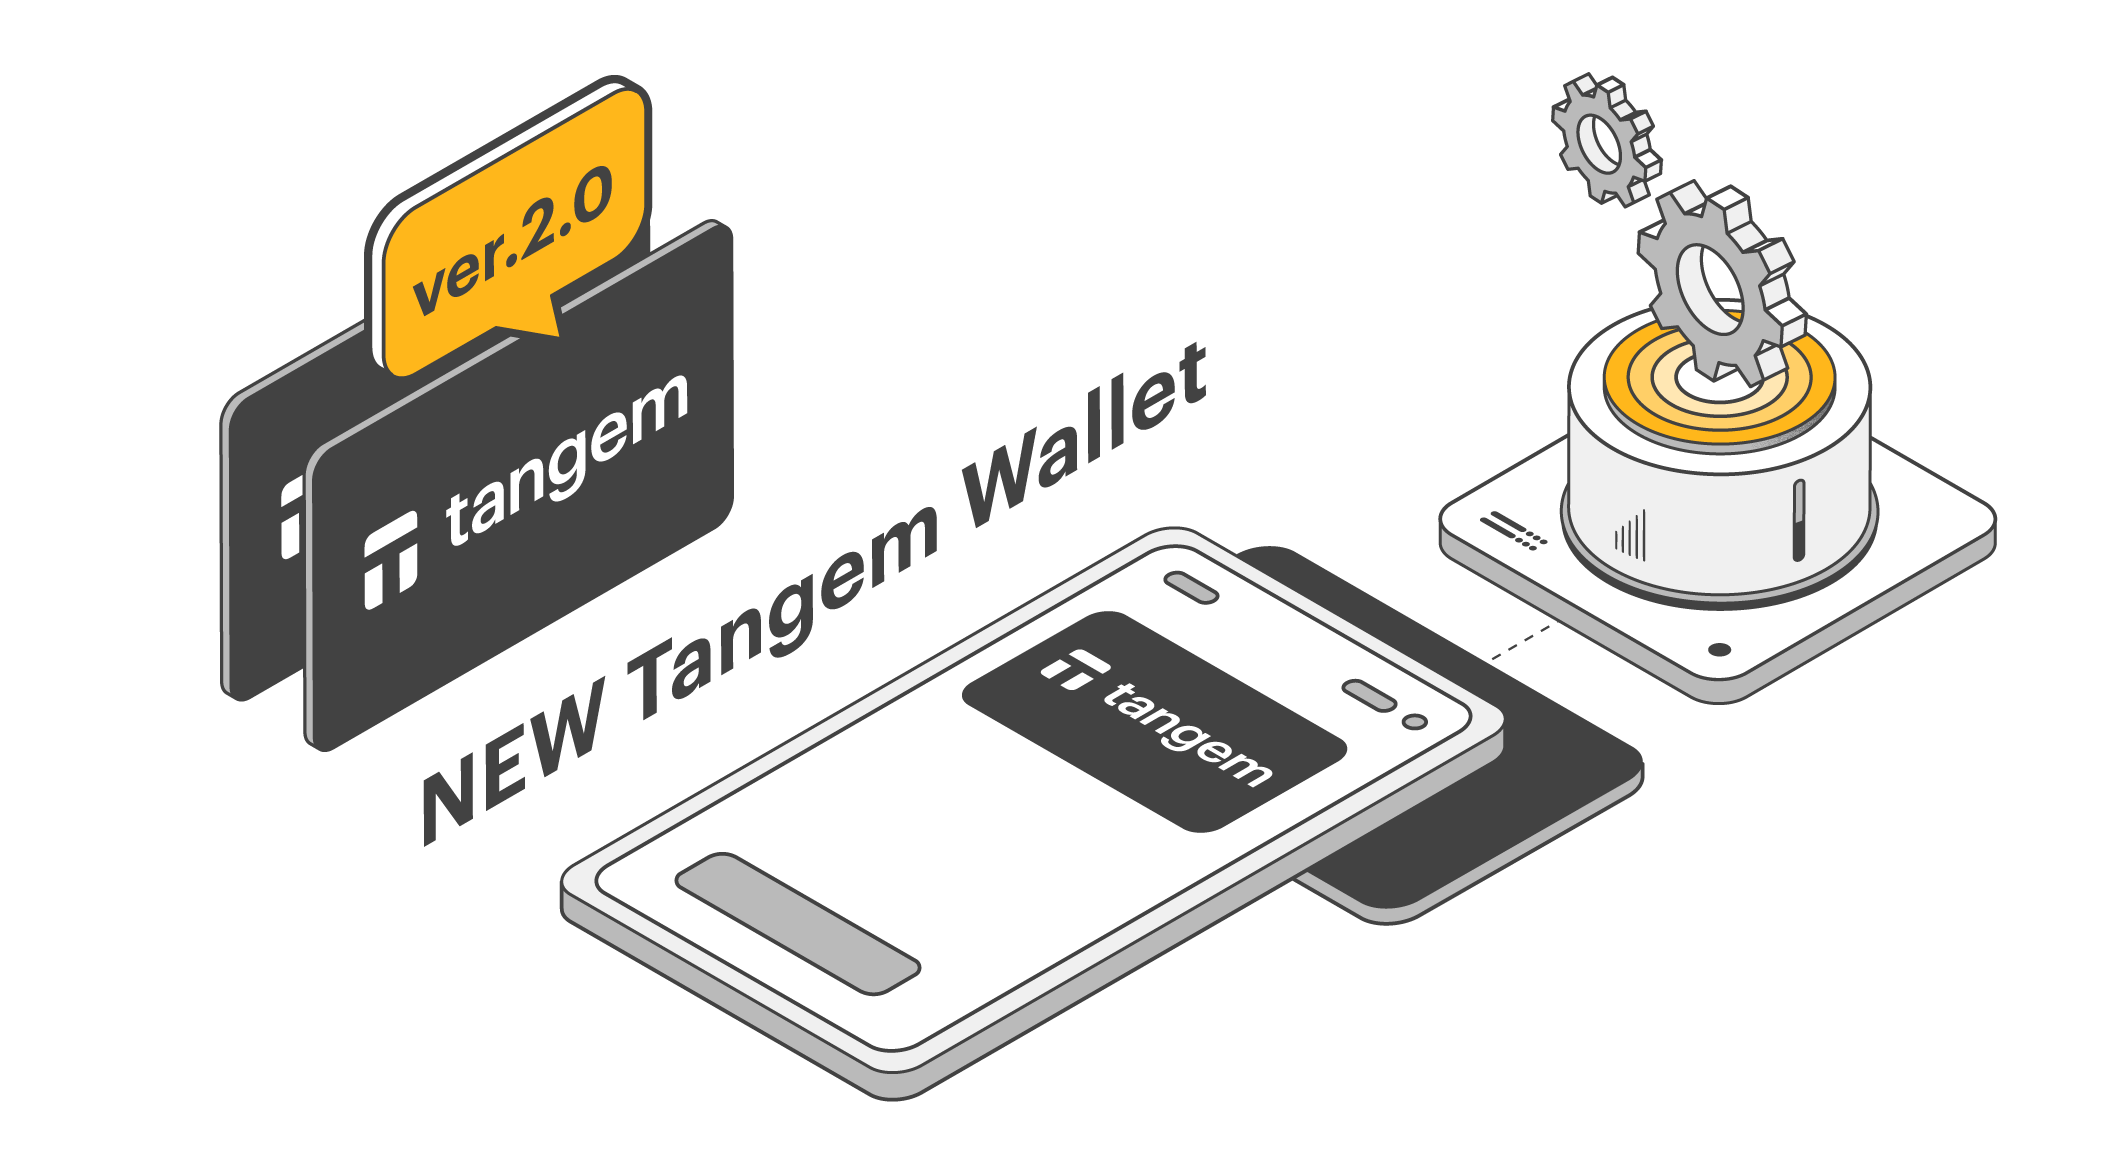
Okay, so check this out—Tangem cards are NFC-enabled hardware wallets embedded in a card.
They hold private keys in secure chips and never expose those keys to the phone or internet.
That means your seed phrase often disappears from the user flow entirely, which is great for people who hate paper seeds.
But wait—there’s a catch: the recovery model isn’t the same as a BIP39 mnemonic by default, and that distinction matters if you plan to pass assets to heirs or migrate later.
My instinct said this might complicate things.
Initially I thought single-card cold storage was perfect for everyday carry.
Then I realized the single-point-of-loss risk—if that card is gone, gone.
On one hand, the card is tamper-evident and robust.
Though actually, without a proper backup strategy you can be locked out forever.
Here’s a quick story.
I once transferred a modest stash to a Tangem for a field test.
A week later I left the card in a jacket pocket that went to the cleaners.
Really? yes. It vanished.
Fortunately I had set up a secondary card as a backup after that scare, and that choice saved me from a real mess.
A clear-eyed look at Tangem’s security model
Tangem cards are built around a secure element chip—kind of like the secure enclave in modern phones but in discrete hardware.
Short version: private keys never leave the chip.
Medium version: the card signs transactions on-chip after you authenticate by NFC from a paired phone or device, and the phone only ever sees the signed transaction.
Longer view: because the attestation and firmware are designed to prevent key extraction, attackers who steal the card still need to bypass hardware protections and any on-card checks, which is non-trivial though not impossible for a powerful adversary with physical lab resources and time.
I’m biased toward hardware-based key storage for long-term holdings.
That said, I worry about how vendors document recovery workflows.
Tangem’s approach favors UX—no visible seed phrases—so novices don’t write down seeds insecurely.
But that UX tradeoff demands you proactively create backups (duplicate cards, multisig, or secure multisig custody) and understand the implications.
If you don’t, the convenience becomes a trap.
Something felt off about how many folks assume “no seed = safer.”
It’s intuitive, but incomplete.
A mnemonic seed is awkward, yes—paper in a shoebox is not sexy—but it is a portable, vendor-agnostic recovery mechanism.
Tangem’s cards can be part of a larger architecture that includes mnemonics or multisignature schemes.
Think of the card as one pillar, not the whole temple.
Practical setups: single card, duplicate card, and multisig
Single card setup is clean.
You buy a card, register it in the app, transfer assets, and you’re done.
Short-term convenience.
But long-term risk: if the card is destroyed or misplaced, recovery depends on the vendor’s supported backup options.
So for anything more than pocket change, consider either purchasing a second card as an exact backup or, better yet, use a multisig strategy where the Tangem is one signer among others.
Multisig deserves extra attention.
It adds complexity, yes—but it also eliminates single points of failure.
Imagine three signers: a Tangem card, a cold-software wallet on a secure laptop, and a custodial cold key held by a trusted party or third-party custody.
You get redundancy and an escape hatch if one device is lost.
But multisig means you also need processes for coordination, recovery, and, crucially, understanding the script-level rules for spending.
I’ll be honest—setting up multisig is a mental overhead for many users.
This part bugs me: industry UX still assumes lots of crypto literacy.
I’m not 100% sure the average user will take the extra step, even though they should.
So a pragmatic middle ground is two Tangem cards kept in separate physical locations (home safe and safety deposit box, for example).
That gives you vendor-friendly UX and a straightforward backup process without learning complex scripts.
Day-to-day use: what feels different
Tapping to sign is fast.
Seriously? it’s borderline pleasant.
No cables, no dongles.
Apps often display a transaction preview and require a tap to confirm on the phone while the card signs via NFC.
On mobile-first days this is unbeatable—fast payments, low friction, and a small learning curve.
But watch out for subtle pitfalls.
NFC requires proximity; your phone needs the right app and sometimes permissions can be finicky.
If your phone dies, you’ll need another device with the app and NFC support to access funds—so store your app credentials and any required authentication securely.
Also be mindful of firmware updates: they can introduce new features or changes in behavior, and while vendors push signed updates through secure channels, the update process itself is an operational step you should plan for.
Comparing Tangem cards to seed-phrase hardware wallets
Both protect keys in isolated hardware.
But the user experience diverges sharply.
Seed-based hardware wallets (like Ledger/Trezor variants) give you a mnemonic backup that is vendor-agnostic.
Tangem trades that for direct-on-card keys and a simpler flow.
So choose based on priorities: do you want portability of recovery (mnemonic) or everyday simplicity (card)?
On one hand, mnemonics feel archaic.
On the other, they are resilient: anyone with the phrase and knowledge can recover across wallets years from now.
I try to keep both worlds in mind—use Tangem for routine cold storage, but store a mnemonic-derived backup in a separate secure location if the assets are long-term and critical.
That way you have both user-friendly access and vendor-agnostic recovery.
Best practices and operational tips
Buy an extra card at purchase.
Seriously—do it.
Store cards separately.
Document who is allowed to access cards and how to act if a card is lost or suspected stolen.
Consider splitting roles: one card for day-to-day operations with low balances, another in deep cold storage for long-term holdings.
Test recovery processes before moving large amounts.
This is basic but often skipped.
Try restoring a small test amount using your planned recovery path to confirm everything works.
Keep firmware and app versions updated on devices you plan to use for signing.
Label cards subtly; do not write private info on them—security through obscurity is not security, but practical labeling helps in emergencies.
Where Tangem fits in your custody strategy
Tangem is ideal for people who prioritize ease of use and physical form-factor.
It’s a great bridge for newcomers and a solid component for seasoned users who layer it into a broader custody plan.
I’m enthusiastic about how it lowers the barrier to secure storage, though cautious about over-reliance on a single vendor or single card.
Balance convenience and redundancy—duplicate cards, multisig, or mnemonic backups are all viable complements.
If you want a quick primer or vendor specifics, check out tangem for product info and setup guides.
Oh, and by the way… practice, documentation, and simple redundancy will save you sleepless nights.
FAQ
Can Tangem cards be hacked if stolen?
They’re engineered to protect keys in a secure element, which raises the bar significantly versus software-only wallets.
That said, sophisticated attackers with physical access and lab equipment could attempt extraction, and supply-chain or firmware attacks are theoretical vectors, so treat lost cards as compromised until proven otherwise.
Do I still need a seed phrase?
Not strictly for day-to-day Tangem use, but a mnemonic remains the most interoperable recovery method.
If you want vendor independence and long-term recoverability, keep a mnemonic or an alternative secure backup strategy in addition to your Tangem cards.
How should I backup my Tangem card?
Best options: buy a duplicate card and store it separately, or use Tangem as one signer in a multisig wallet.
Test your backups and consider legal arrangements (estate planning) for very large holdings.