Whoa!
I was poking around a broken transaction one afternoon and the emotions hit first. My instinct said somethin’ was off. At first it felt like digging through a drawer of receipts — messy, confusing, but oddly satisfying when something clicked. Initially I thought the raw logs would be enough, but then I realized that context matters more than I gave it credit for.
Really?
Yeah. Solana’s transaction model is fast and compact, which is great for throughput but terrible when you’re trying to audit or trace a token flow by hand. You can see a signature and basic meta in seconds. But understanding which instruction did what, and why a token moved two hops then vanished, often requires analytics that stitch things together across slots and inner instructions.
Whoa!
Here’s the thing. Explorers are where intuition meets evidence. A good explorer surfaces the steps in a transaction in a way your brain can follow. It shows you log messages, program accounts, rent exemptions, and inner instructions without making you mentally reassemble bytecode like some kind of reverse engineer. I’m biased, but that usability gap is what separates casual curiosity from real operational insight.
Why I keep returning to Solscan
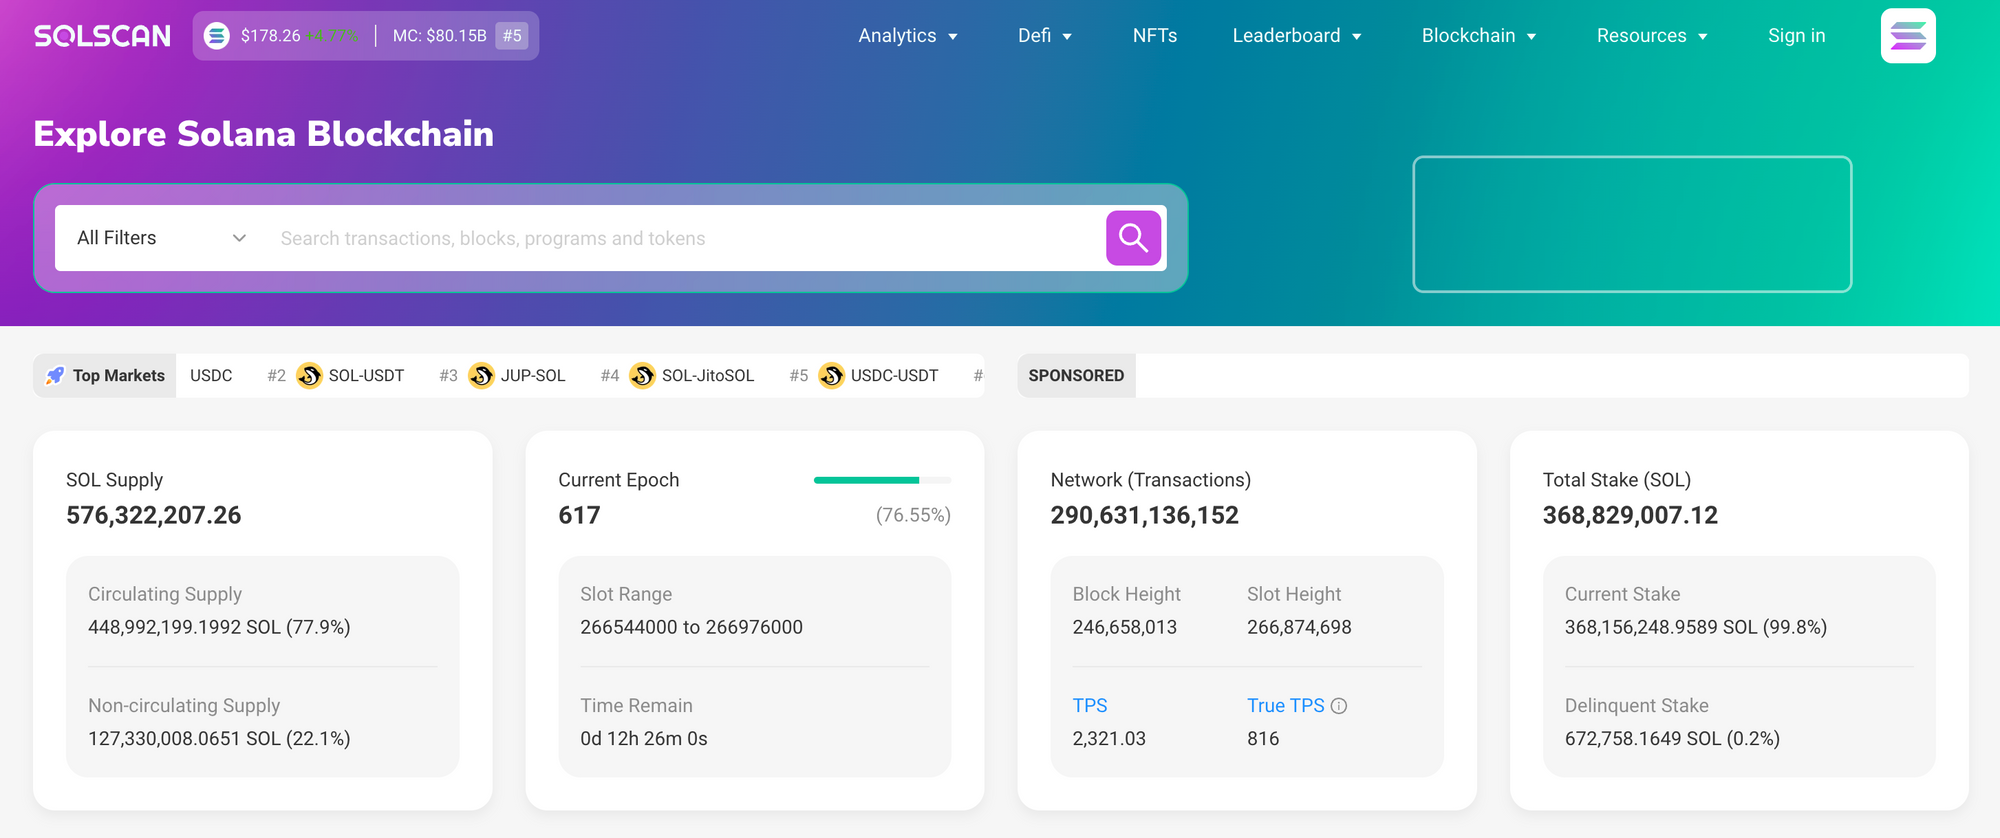
Okay, so check this out—I’ve used multiple Solana explorers, and the one I land on most often is the solscan explorer official site because it balances raw detail with readable summaries. It lays out token transfers clearly, groups inner instructions, and offers a timeline view that helps when transactions include CPI (cross-program invocations). On one hand some explorers try to be minimal and pretty—though actually, those can hide the signals you need; on the other hand, overly verbose interfaces dump everything on you and expect you to be a parser.
Seriously?
Yes. For example, when a Serum trade executes through a DEX, you’ll often see multiple program calls: token transfers, account updates, and program-specific settle instructions. A good explorer will annotate which call belongs to which program and why a particular account’s balance changed. Without those annotations you’re left guessing if a loss was from a swap slippage, a fee, or a bug in a program that mishandled an account.
Hmm…
My approach is pragmatic. I start with the high-level—signatures, slot, timestamp—then dive into the instruction list. If I need to reconcile token balances, I look at pre/post balances and the token transfer events. If things still don’t add up, I read program logs and search for common error strings; sometimes the program itself emits a helpful message that solves the mystery in one line.
Whoa!
Analytics dashboards matter a lot too. Aggregated views like token flow graphs, holder distributions, and historical transaction volumes turn raw transactions into patterns. Those patterns highlight anomalies—sudden spikes in transfer counts, abnormal on-chain activity tied to program upgrades, or clusters of tiny transfers that could be dusting. Detecting such anomalies early can mean the difference between being proactive and playing catch-up.
Okay, so here’s a practical checklist I use when investigating an odd SOL transaction.
1) Confirm signature and slot. Simple but very very important. 2) Check pre/post balances for the involved accounts. 3) Inspect instruction list and map each instruction to a known program. 4) Read program logs for emitted messages or errors. 5) Cross-reference token transfers with token program events.
Really?
Honestly, that checklist is iterative. Initially I thought steps 2 and 3 were enough, but then a mis-specified account owner taught me otherwise. Actually, wait—let me rephrase that: sometimes the difference between a failed transaction and a successful but costly one is a single missing rent exemption or an unexpected PDA derivation, which only shows up when you combine logs with balance deltas.
Hmm…
I should mention tooling. Some dashboards let you filter by program, token mint, or wallet cluster, which speeds up triage. Others provide exportable CSVs; that’s handy when you want to run a local analysis or feed data into a notebook. There are times I export a dozen transactions, run a quick script, and find a repeating pattern that the web UI never made obvious.
Common pitfalls and how to avoid them
Whoa!
One pitfall is assuming that every transfer event is user-initiated. Many are programmatic—settlements, fee distributions, or state migrations. Another is trusting UI-derived labels without verification; some explorers guess program names based on IDs and can be wrong. Double-check when money’s involved. (oh, and by the way…) Backup your findings with on-chain evidence, not just a dashboard screenshot.
Seriously?
Yes—because on-chain data is canonical. If you see a large transfer and the explorer labels it “treasury payout,” dig into the program’s instruction data or repo. Sometimes the label is accurate, sometimes it’s a convenient guess. When you need legal or operational certainty, cite the signature and slot, not a third-party annotation.
I’ll be honest—I don’t catch everything.
There are limits to what explorers can infer. Things like off-chain order matching, oracle-fed logic, or multi-sig signatory intent won’t appear in a transaction record. In those cases you need external context: project announcements, upgrade logs, or governance proposals. I’m not 100% sure about some of these edge behaviors, and that uncertainty is part of responsible analysis.
FAQ
How do I read inner instructions?
Inner instructions are calls made by programs during execution; they show up nested under the main instruction list. Start by identifying the program making the CPI and follow the args—look for token program transfer events and account balance changes to map effects. If logs are present, they often explain intent.
Which explorer should I trust for audits?
Trust no single source. Use an explorer like the one linked above for quick triage, but corroborate with raw RPC calls when accuracy is critical. Audits require both UI-friendly summaries and raw data pulls; treat explorers as your guide, not your single truth.